

Do you know someone who has had an account hacked because of a weak password? Maybe you’ve even had it happen to you.
Passwords are a basic part of our digital lives. They help protect everything from our email and social media accounts to our banking and shopping information. But some common password habits can make it much easier for bad actors to get access.
Here are four password mistakes to avoid—and what you can do instead.
1. Don’t Make Your Password Easy to Guess
Many people use passwords that are too short or base them on family or pet names, hobbies, or publicly searchable information like a home address. Others choose simple patterns that are easy to guess. In these cases, bad actors don’t necessarily need sophisticated technology to figure out your password.
Real-Life Examples
- Donald Trump – In 2020, Dutch security researcher Victor Gevers reported successfully accessing Trump’s Twitter account by guessing “MAGA2020!” on his fifth attempt. Dutch prosecutors later said they believed the access had occurred. The account reportedly did not have 2FA enabled. (BBC News)
- LogicMontior – the tech company was reportedly assigning customers default, weak passwords such as “Welcome@” followed by a number. Attackers used those credentials against customer systems. (TechCrunch)
> The Takeaway: Make Your Passwords Long and Unique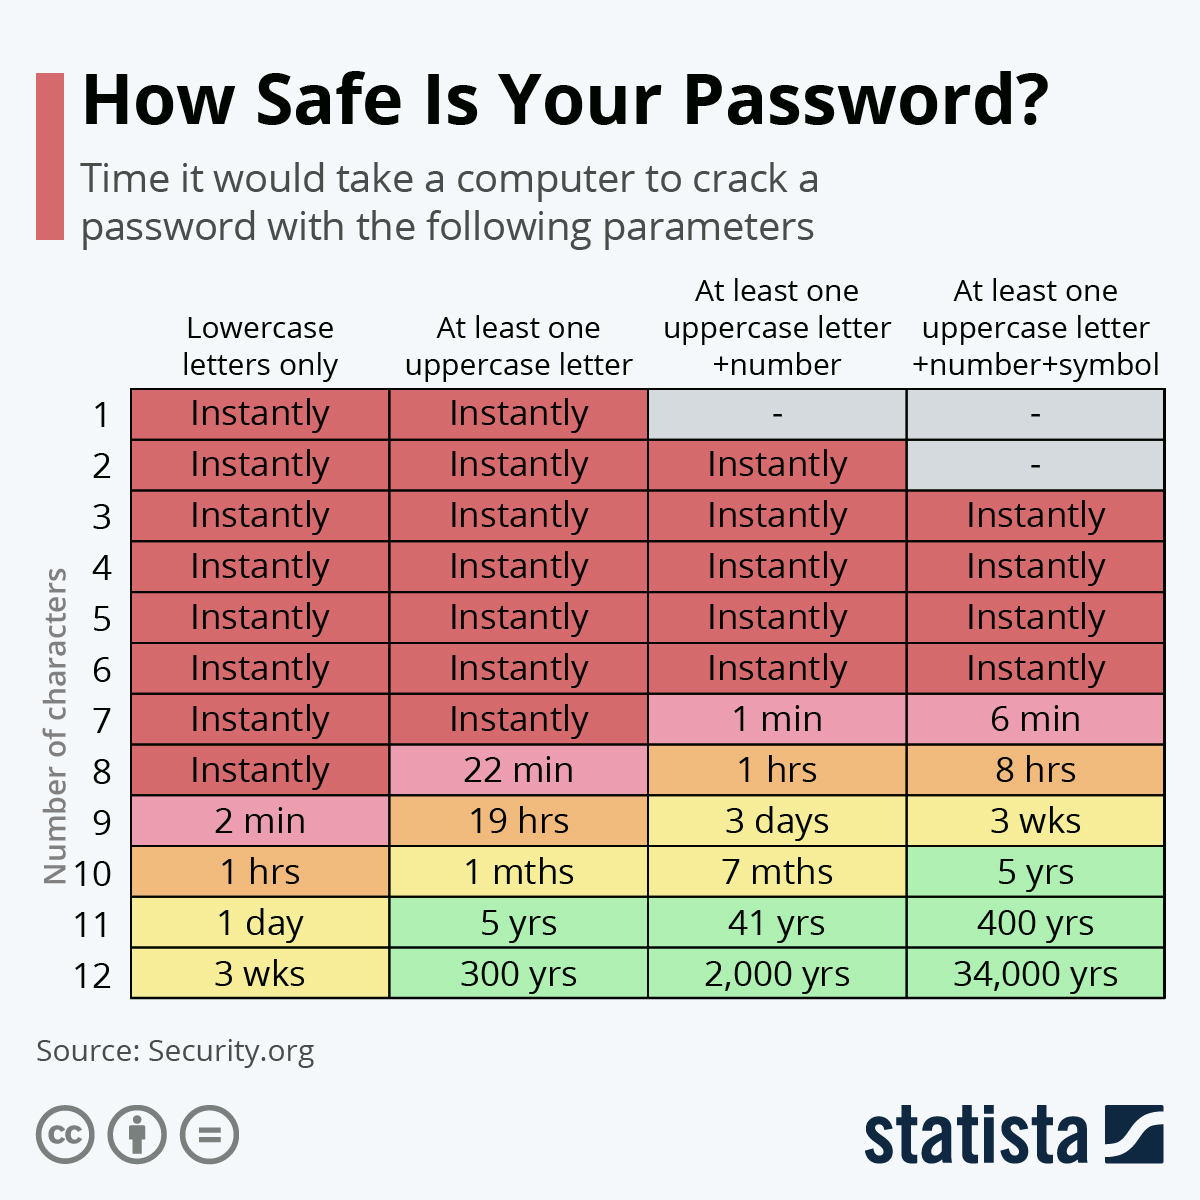
Every password should be
- long – shoot for 16 characters or more
- complex – a mix of letters, numbers, and symbols
- unique – don’t reuse passwords and don’t base them on information about you
Tip: Use a password manager to create and store strong, unique passwords. They are safe and easy to use. If you’re an iOS user, the dedicated Passwords app is a great option. For Android, there’s the equivalent Google Password Manager. But there are also a number of great third-party options that offer free plans, like Proton Pass and Bitwarden.
2. Don’t Reuse Your Passwords
“Reduce, reuse, recycle” might be great advice for the environment, but it’s terrible advice for passwords!
Let’s say you create a password for online banking account. To make things easier, you use that same password for several other websites. If one of those other websites is hacked and your password is exposed, attackers may try that same password on your other accounts—including your bank account.
One stolen password can potentially become the key to multiple accounts.
> The Takeaway: Every Account Gets Its Own Password
You can’t unlock your house by using your car key, right? So don’t unlock your bank account with your email password.
Yes, having a different password for every account means a lot of passwords to keep track of. That’s where a password manager comes in handy. You can use one master password or a passkey to unlock your password vault instead of trying to remember every password individually.
3. Don’t Share Passwords Insecurely
You might have the strongest password in the world. But if you share it with someone who stores it in an email account protected by a poor password, it won’t make a bit of difference.
If you absolutely must share a password, only share it with someone you trust and use a secure method to send it.
> The Takeaway: Keep Passwords Private
Never send a password in an email, text message, or other ordinary messaging app. Those messages may remain stored in your accounts or devices, making the password easier for someone else to find.
Whenever possible, use a password manager’s secure sharing feature instead.
4. Don’t Take the Bait
Unfortunately, sometimes bad actors don’t have to guess your password at all. They simply trick you into giving it to them.
These scams are commonly called phishing. You might receive an email that appears to come from a website, service, friend, or coworker. It may ask you to click a link, open an attachment, or provide information.
The link could take you to a fake website designed to steal your password. An attachment could install malware on your device.
> The Takeaway: Be Skeptical
Watch out for urgency. Scammers want you to react before you have time to think.
Phishing emails and fake websites can look remarkably convincing. If you didn’t initiate the communication, stop and think before providing any information.
You don’t need to click, respond, or answer the phone. You aren’t being rude.
Your best defense isn’t always technology. Sometimes, it’s simply being skeptical.
I’ll have much more to say about phishing in a future article. But next up in our Cybersecurity Awareness Month series, we’ll take a look at multi-factor authentication (MFA) and how it can add another layer of protection to your accounts.
Be sure to check back!
For more information about protecting yourself online, visit staysafeonline.org.
About The Author


